robm1011
Hi
I am a network admin for a small comany.
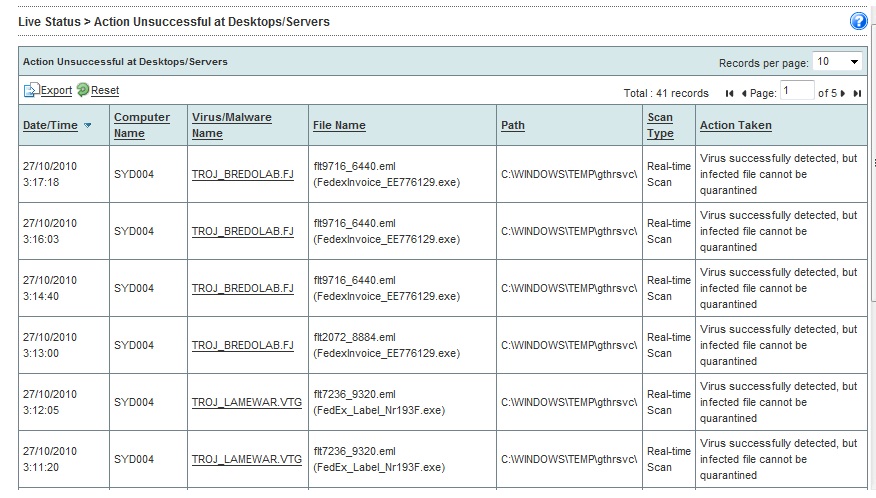
Our Exchange server recently got infected by some malware.
We have Trend Micro installed on all our machines but somehow this thing got through.
I belive it got through in an email it was one of those fedex emails.
so now everyday between 1 and 4 am and pm this thing comes to life and trend is able to quarantine it sometimes.
I have run many diffrent spyware tools on the server but it never finds anything.
Any help would be great.
OS server2003
Hijackthis log
StartupList report, 27/10/2010, 3:26:56 PM
StartupList version: 1.52.2
Started from : C:\malware tools\HijackThis.EXE
Detected: Windows 2003 SP2 (WinNT 5.02.3790)
Detected: Internet Explorer v8.00 (8.00.6001.18702)
* Using default options
* Showing rarely important sections
==================================================
Running processes:
C:\WINDOWS\System32\smss.exe
C:\WINDOWS\system32\winlogon.exe
C:\WINDOWS\system32\services.exe
C:\WINDOWS\system32\lsass.exe
C:\WINDOWS\system32\svchost.exe
C:\WINDOWS\System32\svchost.exe
C:\WINDOWS\system32\spoolsv.exe
C:\Program Files\Symantec\Backup Exec\RAWS\bedbg.exe
C:\Program Files\Quest Software\Big Brother BTF\BBNT\1.08d\bin\bbnt.exe
C:\Program Files\CA\SharedComponents\CA_LIC\lic98rmt.exe
C:\Program Files\CA\SharedComponents\BrightStor\DBAcommon\DBASVR.exe
C:\WINDOWS\System32\svchost.exe
C:\Program Files\System Center Operations Manager 2007\HealthService.exe
C:\WINDOWS\system32\inetsrv\inetinfo.exe
C:\Program Files\CA\SharedComponents\CA_LIC\LogWatNT.exe
C:\Program Files\Trend Micro\Client Server Security Agent\ntrtscan.exe
C:\PROGRA~1\POWERC~1\pcns.exe
C:\Program Files\Trend Micro\Messaging Security Agent\svcGenericHost.exe
C:\Program Files\jvm\bin\java.exe
C:\Program Files\Trend Micro\Messaging Security Agent\SMEX_Master.exe
C:\Program Files\Trend Micro\Messaging Security Agent\svcGenericHost.exe
C:\Program Files\Trend Micro\Messaging Security Agent\SMEX_SystemWatcher.exe
C:\compaq\survey\Surveyor.EXE
C:\hp\hpsmh\bin\smhstart.exe
C:\Program Files\Symantec\Backup Exec\RAWS\beremote.exe
C:\hp\hpsmh\bin\hpsmhd.exe
C:\hp\hpsmh\bin\rotatelogs.exe
C:\hp\hpsmh\bin\rotatelogs.exe
C:\hp\hpsmh\bin\hpsmhd.exe
C:\hp\hpsmh\bin\rotatelogs.exe
C:\hp\hpsmh\bin\rotatelogs.exe
C:\WINDOWS\system32\CpqRcmc.exe
C:\Program Files\Exchsrvr\bin\exmgmt.exe
C:\Program Files\Exchsrvr\bin\mad.exe
C:\Program Files\Common Files\System\MSSearch\Bin\mssearch.exe
C:\WINDOWS\system32\sysdown.exe
C:\Program Files\Trend Micro\Client Server Security Agent\tmlisten.exe
C:\WINDOWS\System32\svchost.exe
c:\windows\system32\inetsrv\w3wp.exe
C:\Program Files\Exchsrvr\bin\store.exe
C:\Program Files\Exchsrvr\bin\emsmta.exe
C:\Program Files\Trend Micro\Client Server Security Agent\CNTAoSMgr.exe
C:\WINDOWS\System32\svchost.exe
C:\WINDOWS\System32\svchost.exe
C:\Program Files\Trend Micro\Client Server Security Agent\TmProxy.exe
C:\WINDOWS\Explorer.EXE
C:\WINDOWS\system32\cpqteam.exe
C:\Program Files\Trend Micro\Client Server Security Agent\pccntmon.exe
C:\WINDOWS\system32\ctfmon.exe
C:\WINDOWS\system32\winlogon.exe
C:\WINDOWS\system32\rdpclip.exe
C:\WINDOWS\Explorer.EXE
C:\WINDOWS\system32\cpqteam.exe
C:\Program Files\Trend Micro\Client Server Security Agent\pccntmon.exe
C:\WINDOWS\system32\ctfmon.exe
c:\windows\system32\inetsrv\w3wp.exe
C:\malware tools\HijackThis.exe
--------------------------------------------------
Checking Windows NT UserInit:
[HKLM\Software\Microsoft\Windows NT\CurrentVersion\Winlogon]
UserInit = C:\WINDOWS\system32\userinit.exe,
--------------------------------------------------
Autorun entries from Registry:
HKLM\Software\Microsoft\Windows\CurrentVersion\Run
CPQTEAM = cpqteam.exe
OfficeScanNT Monitor = "C:\Program Files\Trend Micro\Client Server Security Agent\pccntmon.exe" -HideWindow
DWQueuedReporting = "C:\PROGRA~1\COMMON~1\MICROS~1\DW\dwtrig20.exe" -t
--------------------------------------------------
Autorun entries from Registry:
HKLM\Software\Microsoft\Windows\CurrentVersion\RunOnce
TSC = "C:\Program Files\Trend Micro\Client Server Security Agent\tsc.exe" /HD
--------------------------------------------------
Autorun entries from Registry:
HKCU\Software\Microsoft\Windows\CurrentVersion\Run
ctfmon.exe = C:\WINDOWS\system32\ctfmon.exe
--------------------------------------------------
Enumerating Active Setup stub paths:
HKLM\Software\Microsoft\Active Setup\Installed Components
(* = disabled by HKCU twin)
[<{12d0ed0d-0ee0-4f90-8827-78cefb8f4988}] *
StubPath = C:\WINDOWS\system32\ieudinit.exe
[>{22d6f312-b0f6-11d0-94ab-0080c74c7e95}] *
StubPath = C:\WINDOWS\INF\unregmp2.exe /HideWMP
[>{26923b43-4d38-484f-9b9e-de460746276c}] *
StubPath = C:\WINDOWS\system32\ie4uinit.exe -UserIconConfig
[>{60B49E34-C7CC-11D0-8953-00A0C90347FF}] *
StubPath = "C:\WINDOWS\system32\rundll32.exe" "C:\WINDOWS\system32\iedkcs32.dll",BrandIEActiveSetup SIGNUP
[{2C7339CF-2B09-4501-B3F3-F3508C9228ED}] *
StubPath = %SystemRoot%\system32\regsvr32.exe /s /n /i:/UserInstall %SystemRoot%\system32\themeui.dll
[{36BBA8D2-CA5C-4847-81CC-4F807DD86C91}] *
StubPath = %SystemRoot%\system32\regsvr32.exe /s /n /i:IEUpdateUser urlmon.dll
[{44BBA840-CC51-11CF-AAFA-00AA00B6015C}] *
StubPath = "%ProgramFiles%\Outlook Express\setup50.exe" /APP:OE /CALLER:WINNT /user /install
[{6D69F546-C1AF-4049-AE9E-28627B91D3F5}] *
StubPath = %SystemRoot%\system32\regsvr32.exe /s /n /i:IEUpdateAdmin urlmon.dll
[{7790769C-0471-11d2-AF11-00C04FA35D02}] *
StubPath = "%ProgramFiles%\Outlook Express\setup50.exe" /APP:WAB /CALLER:WINNT /user /install
[{89820200-ECBD-11cf-8B85-00AA005B4340}] *
StubPath = regsvr32.exe /s /n /i:U shell32.dll
[{89820200-ECBD-11cf-8B85-00AA005B4383}] *
StubPath = C:\WINDOWS\system32\ie4uinit.exe -BaseSettings
[{89B4C1CD-B018-4511-B0A1-5476DBF70820}] *
StubPath = C:\WINDOWS\system32\Rundll32.exe C:\WINDOWS\system32\mscories.dll,Install
[{A509B1A7-37EF-4b3f-8CFC-4F3A74704073}]
StubPath = %SystemRoot%\system32\rundll32.exe iesetup.dll,IEHardenAdmin
[{A509B1A8-37EF-4b3f-8CFC-4F3A74704073}]
StubPath = %SystemRoot%\system32\rundll32.exe iesetup.dll,IEHardenUser
--------------------------------------------------
Shell & screensaver key from C:\WINDOWS\SYSTEM.INI:
Shell=*INI section not found*
SCRNSAVE.EXE=*INI section not found*
drivers=*INI section not found*
Shell & screensaver key from Registry:
Shell=Explorer.exe
SCRNSAVE.EXE=
drivers=*Registry value not found*
Policies Shell key:
HKCU\..\Policies: Shell=*Registry value not found*
HKLM\..\Policies: Shell=*Registry value not found*
--------------------------------------------------
Checking for EXPLORER.EXE instances:
C:\WINDOWS\Explorer.exe: PRESENT!
C:\Explorer.exe: not present
C:\WINDOWS\Explorer\Explorer.exe: not present
C:\WINDOWS\System\Explorer.exe: not present
C:\WINDOWS\System32\Explorer.exe: not present
C:\WINDOWS\Command\Explorer.exe: not present
C:\WINDOWS\Fonts\Explorer.exe: not present
--------------------------------------------------
Checking for superhidden extensions:
.lnk: HIDDEN! (arrow overlay: yes)
.pif: HIDDEN! (arrow overlay: yes)
.exe: not hidden
.com: not hidden
.bat: not hidden
.hta: not hidden
.scr: not hidden
.shs: HIDDEN!
.shb: HIDDEN!
.vbs: not hidden
.vbe: not hidden
.wsh: not hidden
.scf: HIDDEN! (arrow overlay: NO!)
.url: HIDDEN! (arrow overlay: yes)
.js: not hidden
.jse: not hidden
--------------------------------------------------
Enumerating Browser Helper Objects:
Trend Micro NSC BHO - C:\Program Files\Trend Micro\Client Server Security Agent\bho\1009\TmIEPlg.dll - {1CA1377B-DC1D-4A52-9585-6E06050FAC53}
--------------------------------------------------
Enumerating Task Scheduler jobs:
SYD004SYS.job
--------------------------------------------------
Enumerating Windows NT/2000/XP services
Application Experience Lookup Service: %SystemRoot%\system32\svchost.exe -k netsvcs (autostart)
Windows Audio: %SystemRoot%\System32\svchost.exe -k netsvcs (autostart)
Backup Exec Remote Agent for Windows Systems: "C:\Program Files\Symantec\Backup Exec\RAWS\beremote.exe" (autostart)
Backup Exec Error Recording Service: "C:\Program Files\Symantec\Backup Exec\RAWS\bedbg.exe" --s (autostart)
Big Brother SNM Client 1.08d: C:\Program Files\Quest Software\Big Brother BTF\BBNT\1.08d\bin\bbnt.exe (autostart)
Computer Browser: %SystemRoot%\system32\svchost.exe -k netsvcs (autostart)
CA License Client: "C:\Program Files\CA\SharedComponents\CA_LIC\lic98rmt.exe" (autostart)
Certificate Services: C:\WINDOWS\system32\certsrv.exe (autostart)
HP ProLiant Remote Monitor Service: %SystemRoot%\system32\CpqRcmc.exe (autostart)
Cryptographic Services: %SystemRoot%\system32\svchost.exe -k netsvcs (autostart)
CA BrightStor Backup Agent RPC Server: "C:\Program Files\CA\SharedComponents\BrightStor\DBAcommon\DBASVR.exe" (autostart)
DCOM Server Process Launcher: %SystemRoot%\system32\svchost.exe -k DcomLaunch (autostart)
DHCP Client: %SystemRoot%\system32\svchost.exe -k NetworkService (autostart)
Logical Disk Manager: %SystemRoot%\System32\svchost.exe -k netsvcs (autostart)
DNS Client: %SystemRoot%\system32\svchost.exe -k NetworkService (autostart)
Error Reporting Service: %SystemRoot%\System32\svchost.exe -k WinErr (autostart)
Event Log: %SystemRoot%\system32\services.exe (autostart)
COM+ Event System: C:\WINDOWS\system32\svchost.exe -k netsvcs (autostart)
EXIFS: \??\C:\WINDOWS\system32\drivers\exifs.sys (autostart)
System Center Management: "C:\Program Files\System Center Operations Manager 2007\HealthService.exe" (autostart)
Help and Support: %SystemRoot%\System32\svchost.exe -k netsvcs (autostart)
IIS Admin Service: C:\WINDOWS\system32\inetsrv\inetinfo.exe (autostart)
Microsoft Exchange IMAP4: C:\WINDOWS\system32\inetsrv\inetinfo.exe (autostart)
Server: %SystemRoot%\system32\svchost.exe -k netsvcs (autostart)
Workstation: %SystemRoot%\system32\svchost.exe -k netsvcs (autostart)
TCP/IP NetBIOS Helper: %SystemRoot%\system32\svchost.exe -k LocalService (autostart)
Event Log Watch: "C:\Program Files\CA\SharedComponents\CA_LIC\LogWatNT.exe" (autostart)
Messenger: %SystemRoot%\system32\svchost.exe -k netsvcs (autostart)
Distributed Transaction Coordinator: C:\WINDOWS\system32\msdtc.exe (autostart)
Microsoft Exchange Information Store: "C:\Program Files\Exchsrvr\bin\store.exe" (autostart)
Microsoft Exchange Management: "C:\Program Files\Exchsrvr\bin\exmgmt.exe" (autostart)
Microsoft Exchange MTA Stacks: "C:\Program Files\Exchsrvr\bin\emsmta.exe" (autostart)
Microsoft Exchange System Attendant: "C:\Program Files\Exchsrvr\bin\mad.exe" (autostart)
FTP Publishing Service: %SystemRoot%\system32\inetsrv\inetinfo.exe (autostart)
Microsoft Search: "C:\Program Files\Common Files\System\MSSearch\Bin\mssearch.exe" (autostart)
Net Logon: %SystemRoot%\system32\lsass.exe (autostart)
Trend Micro Client/Server Security Agent RealTime Scan: "C:\Program Files\Trend Micro\Client Server Security Agent\ntrtscan.exe" (autostart)
Plug and Play: %SystemRoot%\system32\services.exe (autostart)
IPSEC Services: %SystemRoot%\system32\lsass.exe (autostart)
PowerChute Network Shutdown: C:\PROGRA~1\POWERC~1\pcns.exe (autostart)
Protected Storage: %SystemRoot%\system32\lsass.exe (autostart)
Remote Registry: %SystemRoot%\system32\svchost.exe -k regsvc (autostart)
Microsoft Exchange Routing Engine: C:\WINDOWS\system32\inetsrv\inetinfo.exe (autostart)
Remote Procedure Call (RPC): %SystemRoot%\system32\svchost.exe -k rpcss (autostart)
Security Accounts Manager: %SystemRoot%\system32\lsass.exe (autostart)
Trend Micro Messaging Security Agent Master Service: "C:\Program Files\Trend Micro\Messaging Security Agent\svcGenericHost.exe" SMEX_Master.exe .\config\cfg_ipcServerDll1.txt SMEX_HOST (autostart)
Trend Micro Messaging Security Agent Remote Configuration Server: "C:\Program Files\Trend Micro\Messaging Security Agent\svcGenericHost.exe" SMEX_RemoteConfig.exe .\config\cfg_ipcServerDll2.txt SMEX_CFG_HOST (autostart)
Trend Micro Messaging Security Agent System Watcher: "C:\Program Files\Trend Micro\Messaging Security Agent\svcGenericHost.exe" SMEX_SystemWatcher.exe .\config\cfg_SystemWatcherManager.txt SMEX_SW (autostart)
Task Scheduler: %SystemRoot%\System32\svchost.exe -k netsvcs (autostart)
Secondary Logon: %SystemRoot%\System32\svchost.exe -k netsvcs (autostart)
System Event Notification: %SystemRoot%\system32\svchost.exe -k netsvcs (autostart)
Shell Hardware Detection: %SystemRoot%\System32\svchost.exe -k netsvcs (autostart)
Simple Mail Transfer Protocol (SMTP): C:\WINDOWS\system32\inetsrv\inetinfo.exe (autostart)
Print Spooler: %SystemRoot%\system32\spoolsv.exe (autostart)
Surveyor: C:\compaq\survey\Surveyor.EXE (autostart)
HP ProLiant System Shutdown Service: %SystemRoot%\system32\sysdown.exe (autostart)
HP System Management Homepage: C:\hp\hpsmh\bin\smhstart.exe (autostart)
tmcomm: \??\C:\WINDOWS\system32\drivers\tmcomm.sys (autostart)
Trend Micro Filter: \??\C:\Program Files\Trend Micro\Client Server Security Agent\TmXPFlt.sys (autostart)
Trend Micro Client/Server Security Agent Listener: "C:\Program Files\Trend Micro\Client Server Security Agent\tmlisten.exe" (autostart)
Trend Micro PreFilter: \??\C:\Program Files\Trend Micro\Client Server Security Agent\TmPreFlt.sys (autostart)
Distributed Link Tracking Client: %SystemRoot%\system32\svchost.exe -k netsvcs (autostart)
Trend Micro VSAPI NT: \??\C:\Program Files\Trend Micro\Client Server Security Agent\VSApiNt.sys (autostart)
Windows Time: %SystemRoot%\system32\svchost.exe -k LocalService (autostart)
World Wide Web Publishing Service: %SystemRoot%\System32\svchost.exe -k iissvcs (autostart)
Windows Management Instrumentation: %systemroot%\system32\svchost.exe -k netsvcs (autostart)
Automatic Updates: %systemroot%\system32\svchost.exe -k netsvcs (autostart)
Wireless Configuration: %SystemRoot%\System32\svchost.exe -k netsvcs (autostart)
--------------------------------------------------
Enumerating Windows NT logon/logoff scripts:
*No scripts set to run*
Windows NT checkdisk command:
BootExecute = autocheck autochk *
Windows NT 'Wininit.ini':
PendingFileRenameOperations: C:\WINDOWS\system32\SET4.tmp => C:\WINDOWS\system32\kdcsvc.dll||?
--------------------------------------------------
Enumerating ShellServiceObjectDelayLoad items:
PostBootReminder: C:\WINDOWS\system32\SHELL32.dll
CDBurn: C:\WINDOWS\system32\SHELL32.dll
WebCheck: C:\WINDOWS\system32\webcheck.dll
SysTray: C:\WINDOWS\system32\stobject.dll
--------------------------------------------------
End of report, 14,975 bytes
Report generated in 0.125 seconds
Command line options:
/verbose - to add additional info on each section
/complete - to include empty sections and unsuspicious data
/full - to include several rarely-important sections
/force9x - to include Win9x-only startups even if running on WinNT
/forcent - to include WinNT-only startups even if running on Win9x
/forceall - to include all Win9x and WinNT startups, regardless of platform
/history - to list version history only